This is an automated email from the ASF dual-hosted git repository.

Yilialinn pushed a commit to branch codex/strengthen-apisix-authority-signals
in repository https://gitbox.apache.org/repos/asf/apisix-website.git
commit 5202c14ee3c6371bec00cbc7ebfa7d895d9a682b Author: Yilia Lin <[email protected]> AuthorDate: Fri Sep 18 14:30:52 2026 +0800 docs(seo): add contextual links to learning center guides --- blog/en/blog/2022/07/06/use-keycloak-with-api-gateway-to-secure-apis.md | 2 ++ blog/en/blog/2023/03/23/mtls-everywhere.md | 2 +- blog/en/blog/2023/08/14/rate-limit.md | 2 ++ blog/en/blog/2023/10/18/ingress-apisix.md | 2 ++ blog/en/blog/2024/02/13/apisix-owasp-coraza-core-ruleset.md | 2 ++ blog/en/blog/2025/02/21/why-reinvent-api-gateways.md | 2 ++ 6 files changed, 11 insertions(+), 1 deletion(-) diff --git a/blog/en/blog/2022/07/06/use-keycloak-with-api-gateway-to-secure-apis.md b/blog/en/blog/2022/07/06/use-keycloak-with-api-gateway-to-secure-apis.md index 88360462edd..05955f7a81f 100644 --- a/blog/en/blog/2022/07/06/use-keycloak-with-api-gateway-to-secure-apis.md +++ b/blog/en/blog/2022/07/06/use-keycloak-with-api-gateway-to-secure-apis.md @@ -26,6 +26,8 @@ image: https://static.apiseven.com/2022/blog/0818/plugins/keycloak.png OpenID Connect referred to as OIDC, is an authentication protocol based on the OAuth 2.0. It allows the client to obtain user information from the identity provider (IdP), e.g., Keycloak, Ory, Okta, Auth0, etc. The open-source API Gateway Apache APISIX supports using the [openid-connect plugin](https://apisix.apache.org/docs/apisix/plugins/openid-connect) to integrate with the above identity Providers. It will redirect all unauthenticated clients to IdP's login page. After the successful [...] +OIDC is one of several ways to verify callers at the gateway. The [API gateway authentication guide](/learning-center/api-gateway-authentication/) compares OIDC with API keys, JWT, OAuth 2.0-based flows, mTLS, and HMAC so teams can choose a method before implementing a provider-specific flow. + 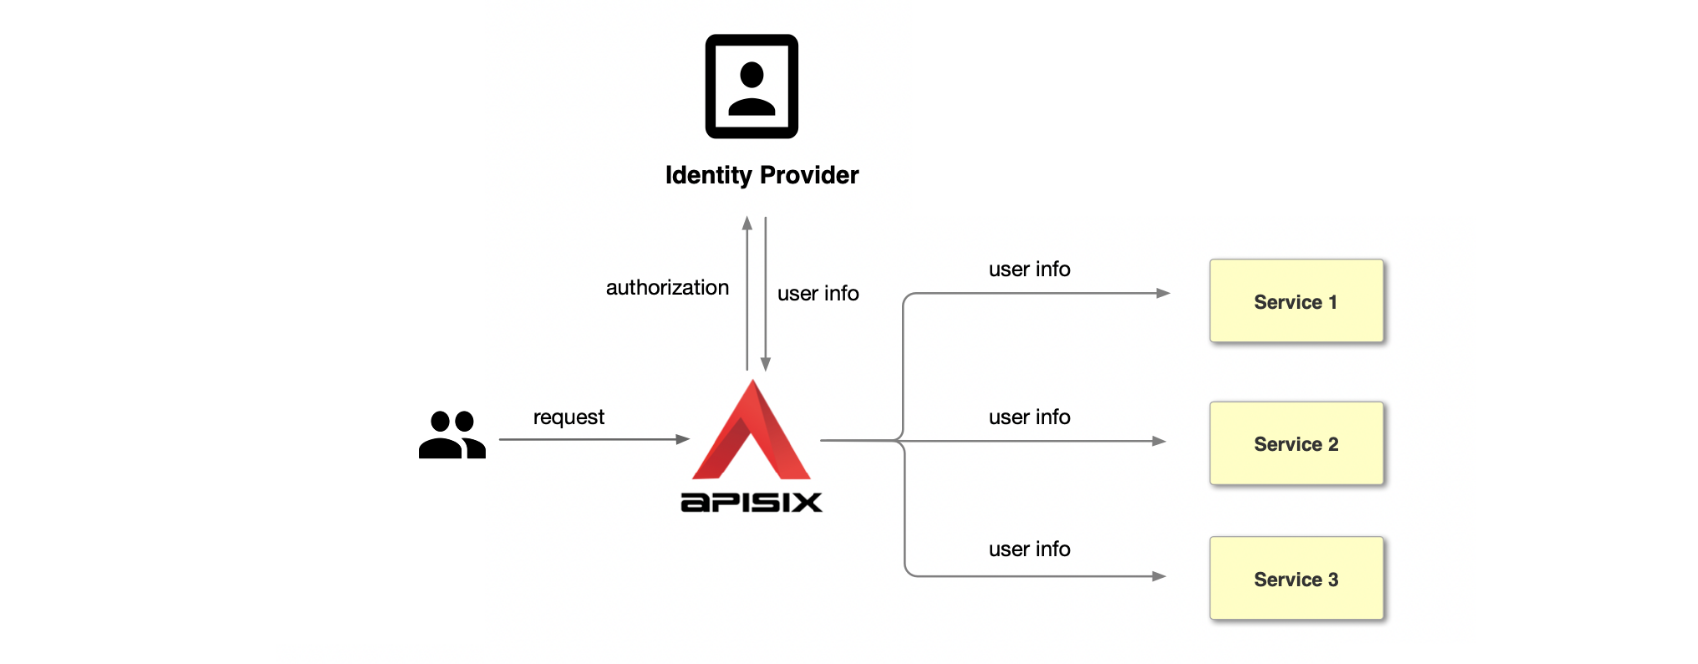 Keycloak is an open-source identity and access management. It adds authentication to applications and secures services with minimum effort. Also, it provides user federation, strong authentication, user management, fine-grained authorization, and more. In this post, we will take [Keycloak](https://www.keycloak.org/docs/latest/securing_apps/) as an example, and let's see how to integrate it with APISIX to protect your services. diff --git a/blog/en/blog/2023/03/23/mtls-everywhere.md b/blog/en/blog/2023/03/23/mtls-everywhere.md index 1378f187518..7306d168605 100644 --- a/blog/en/blog/2023/03/23/mtls-everywhere.md +++ b/blog/en/blog/2023/03/23/mtls-everywhere.md @@ -32,7 +32,7 @@ TLS works through certificates. A certificate is similar to an ID, proving the c TLS authentication is based on public key cryptography. Alice generates a public key/private key pair and publishes the public key. If one encrypts data with the public key, only the private key that generated the public key can decrypt them. The other usage is for one to encrypt data with the private key and everybody with the public key to decrypt it, thus proving their identity. -Finally, mutual TLS, _aka_ mTLS, is the configuration of two-way TLS: server authentication to the client, as usual, but also the other way around, client authentication to the server. +Finally, [mutual TLS (mTLS)](/learning-center/what-is-mutual-tls/) is the configuration of two-way TLS: server authentication to the client, as usual, but also the other way around, client authentication to the server. We now have enough understanding of the concepts to get our hands dirty. diff --git a/blog/en/blog/2023/08/14/rate-limit.md b/blog/en/blog/2023/08/14/rate-limit.md index ce2fdfc4f67..fd2c6f8ff93 100644 --- a/blog/en/blog/2023/08/14/rate-limit.md +++ b/blog/en/blog/2023/08/14/rate-limit.md @@ -26,6 +26,8 @@ Rate limiting can also be part of your business requirement where you want separ If you are using [Apache APISIX](https://apisix.apache.org) as your API gateway, you can leverage the rate limiting plugins, [limit-req](https://apisix.apache.org/docs/apisix/plugins/limit-req/), [limit-conn](https://apisix.apache.org/docs/apisix/plugins/limit-conn/), and [limit-count](https://apisix.apache.org/docs/apisix/plugins/limit-count/) to achieve this. +Before choosing a plugin, review the [API gateway rate limiting guide](/learning-center/api-gateway-rate-limiting/) for the tradeoffs among request rate, request count, concurrency, quota, and distributed-counter strategies. + You can always set this up in your services directly without configuring it in APISIX. But as the number of your services increases, with each service having different constraints, setting up and managing different rate limits and updating them in each of these services becomes a pain point for development teams. In this article, we will look at examples of how we can use the rate limiting plugins in APISIX. You can find the complete configuration files and instructions to deploy for this article in [this repository](https://github.com/navendu-pottekkat/rate-limit). diff --git a/blog/en/blog/2023/10/18/ingress-apisix.md b/blog/en/blog/2023/10/18/ingress-apisix.md index 00bb0aabad4..90e61758140 100644 --- a/blog/en/blog/2023/10/18/ingress-apisix.md +++ b/blog/en/blog/2023/10/18/ingress-apisix.md @@ -26,6 +26,8 @@ image: https://static.apiseven.com/2022/10/19/634f6677742a1.png APISIX Ingress Controller is a Kubernetes Ingress Controller based on Apache APISIX. It has the capability to convert Ingress/CRDs resources from Kubernetes into routing rules for Apache APISIX, synchronizing them with the Apache APISIX cluster. As a result, users can harness the robust functionalities of Apache APISIX, including plugins, load balancing, health checks, and more, for the management of inbound traffic in Kubernetes. +For a current overview of Ingress, Gateway API, and controller selection, see the [Kubernetes API gateway guide](/learning-center/kubernetes-api-gateway/). This article continues with the architecture introduced in APISIX Ingress Controller 1.7.0. + 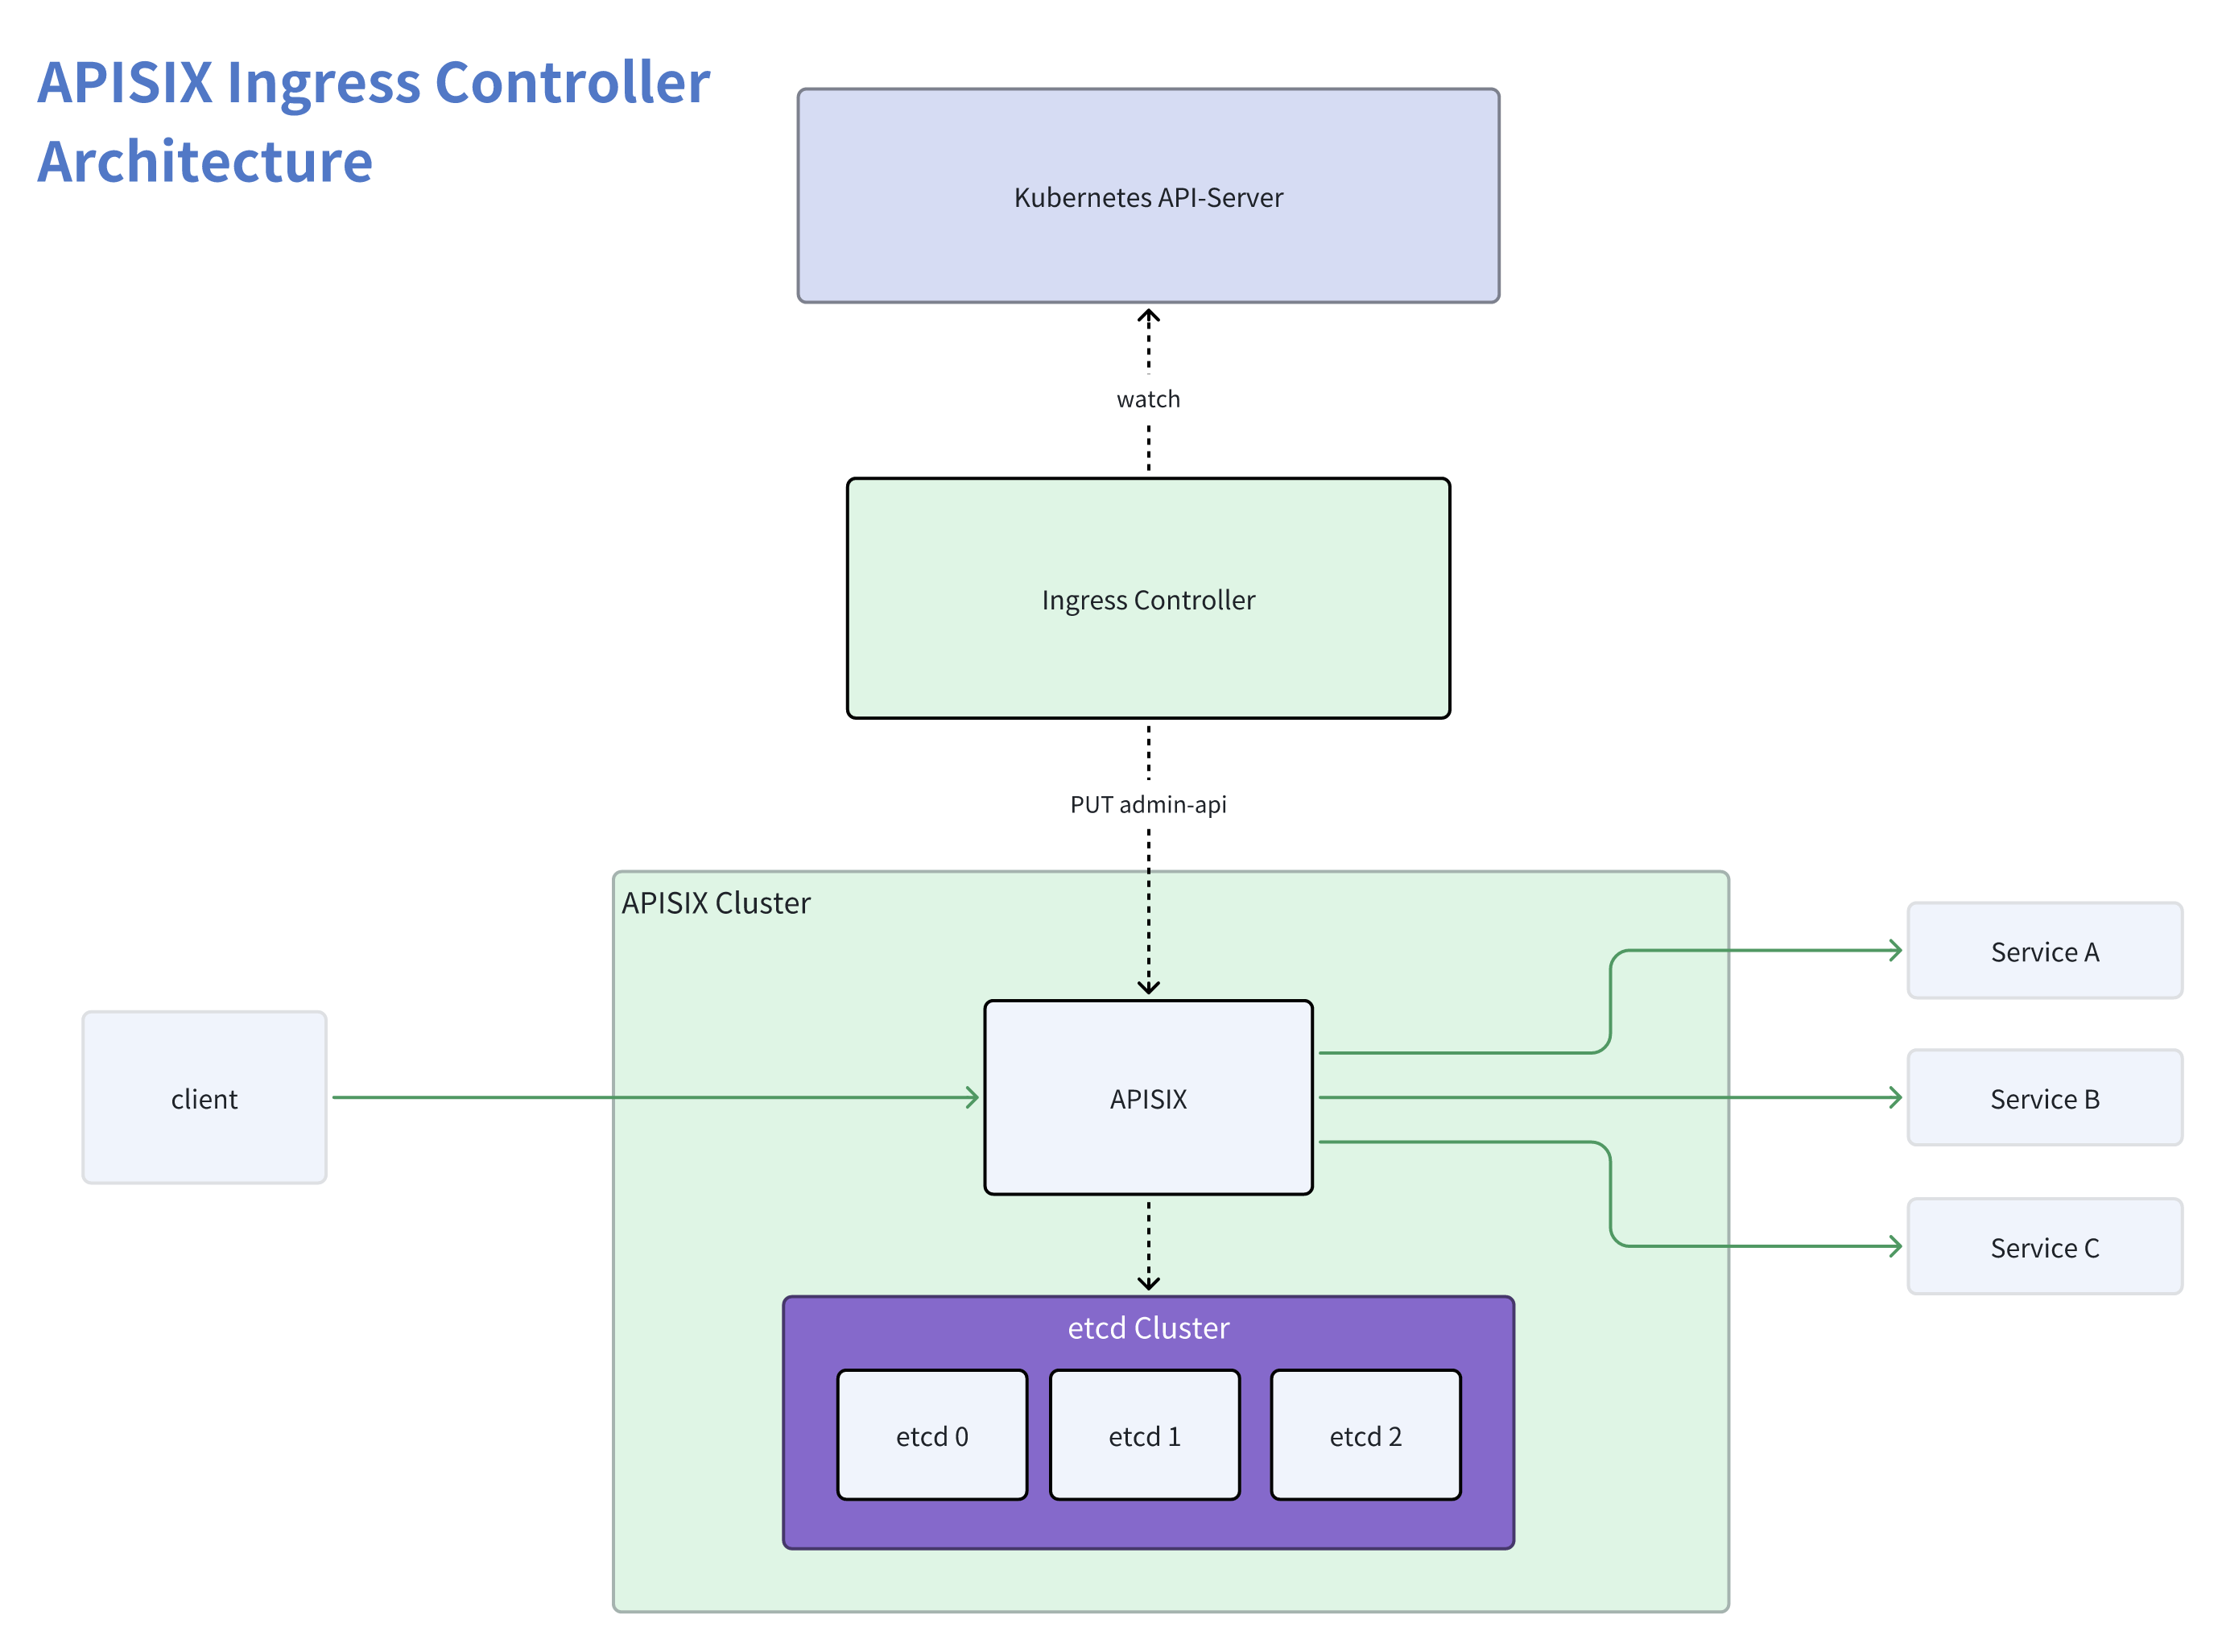 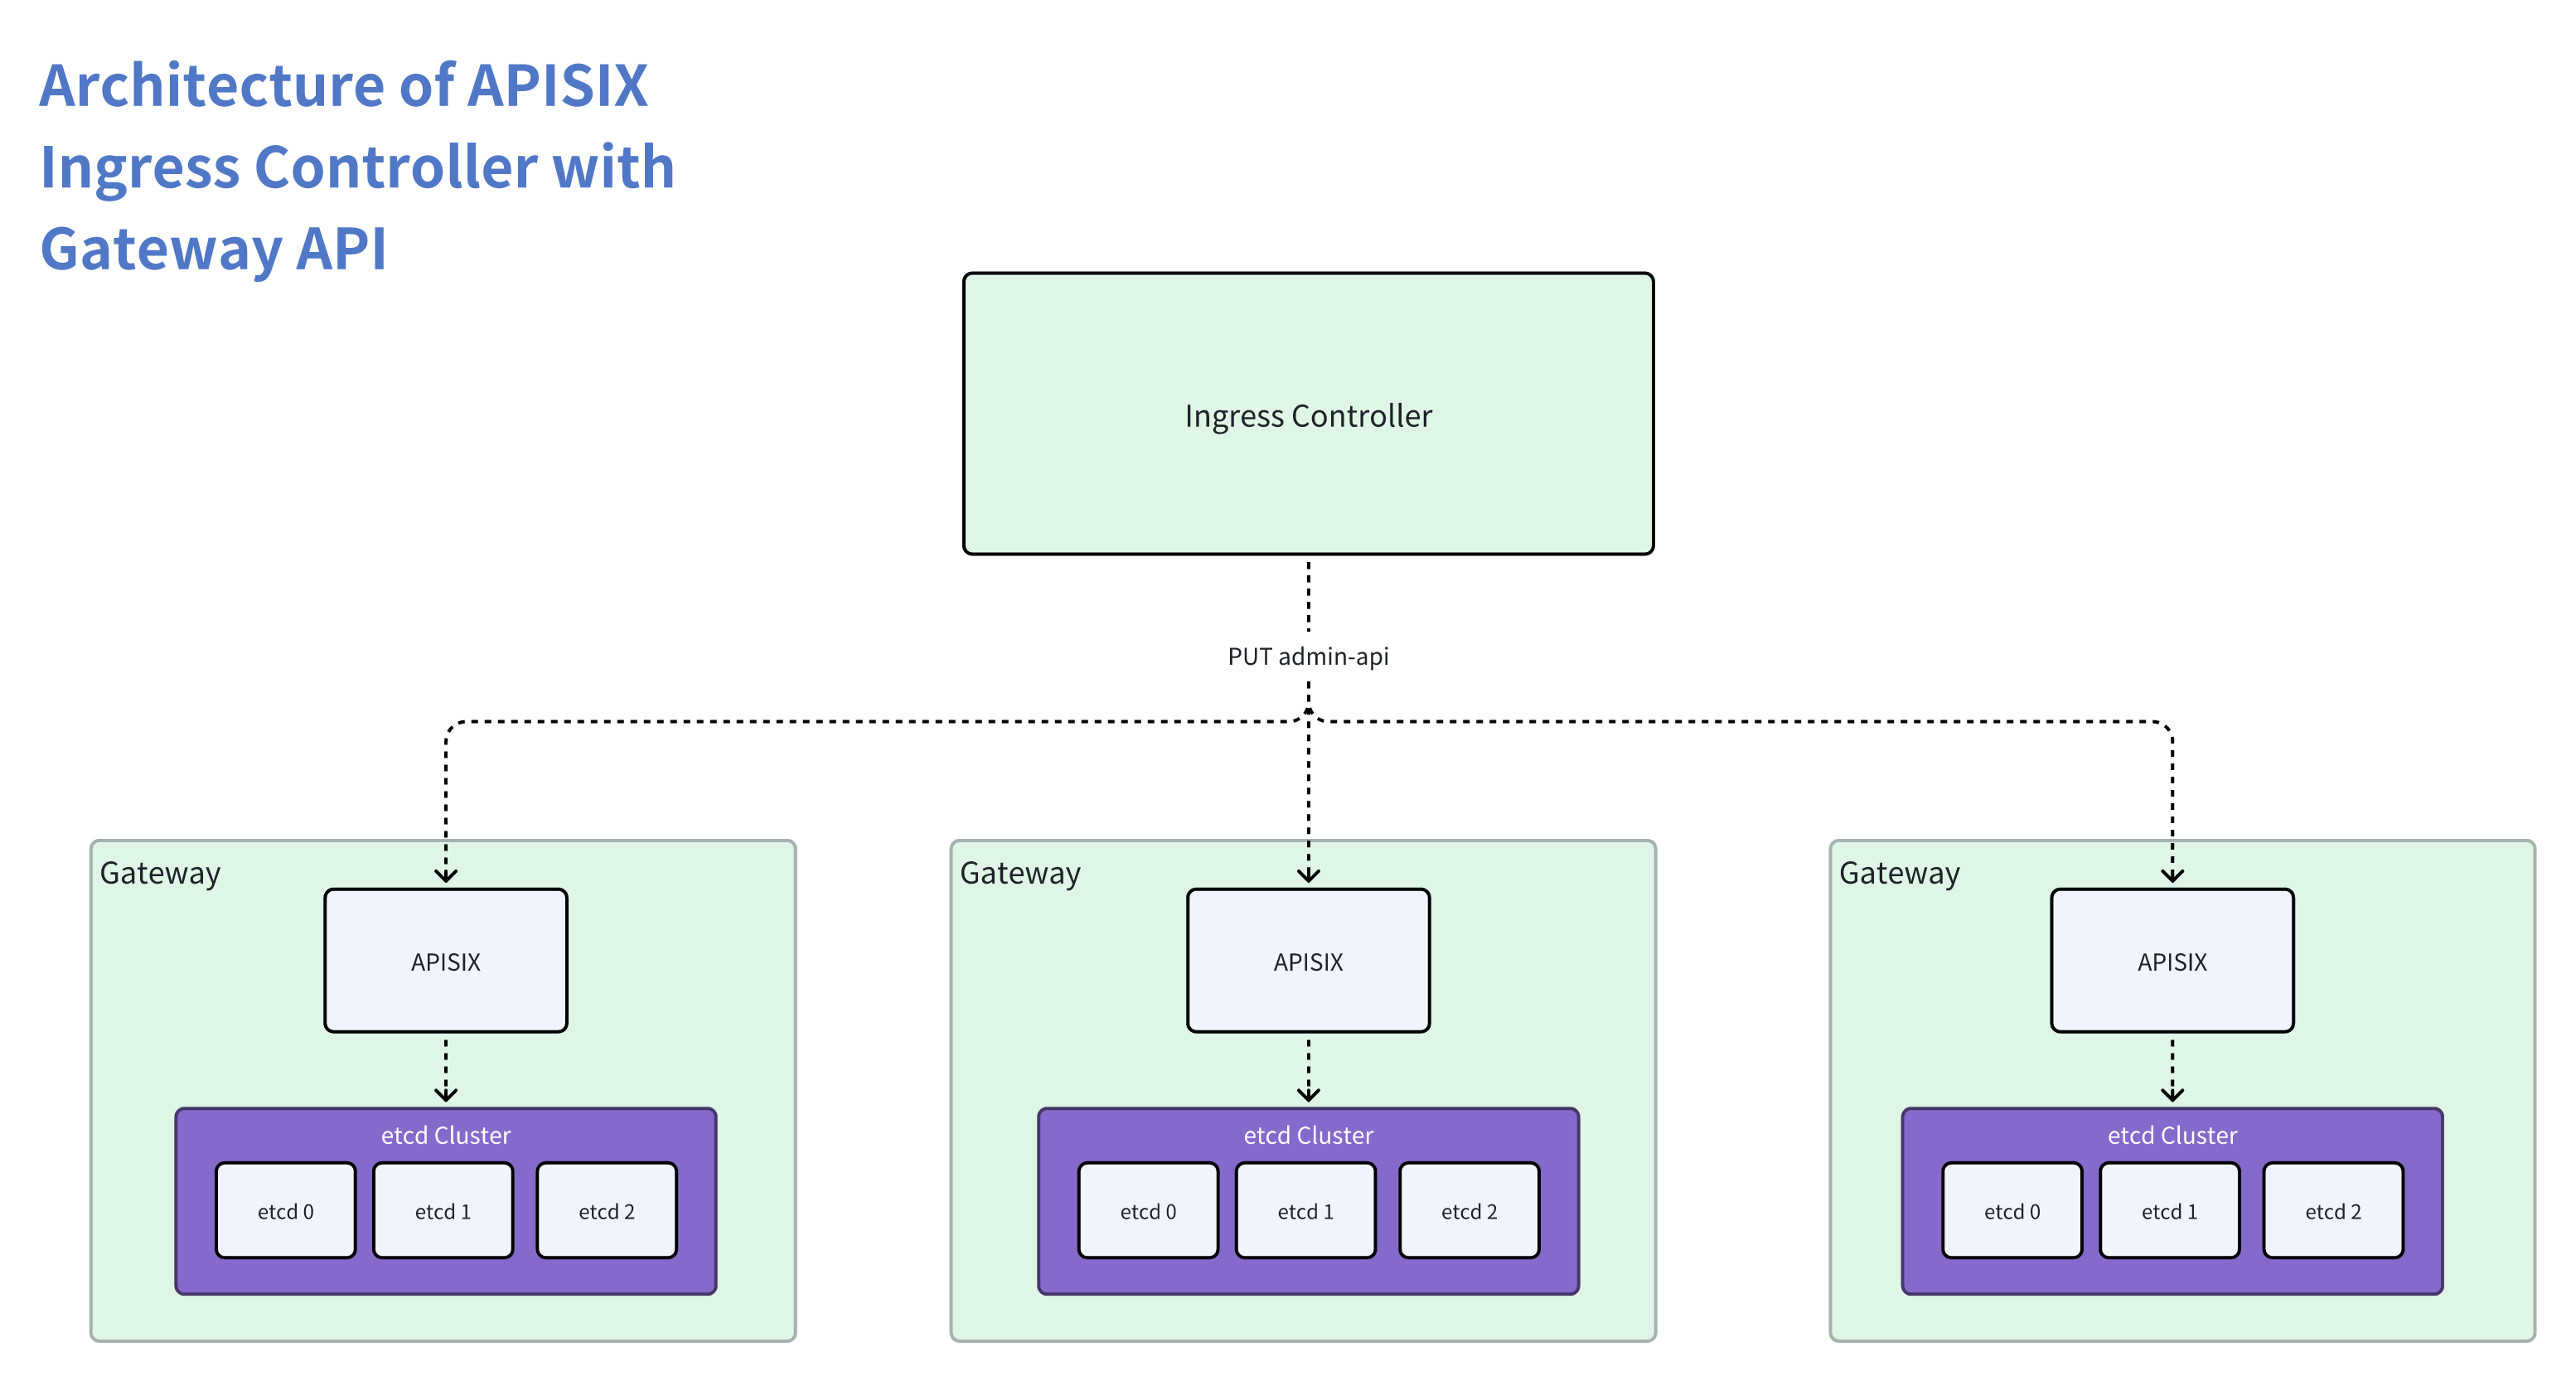 diff --git a/blog/en/blog/2024/02/13/apisix-owasp-coraza-core-ruleset.md b/blog/en/blog/2024/02/13/apisix-owasp-coraza-core-ruleset.md index b8f982445a8..57971b61019 100644 --- a/blog/en/blog/2024/02/13/apisix-owasp-coraza-core-ruleset.md +++ b/blog/en/blog/2024/02/13/apisix-owasp-coraza-core-ruleset.md @@ -37,6 +37,8 @@ For more details, please check the complete [report](https://owasp.org/www-proje Fixing a vulnerability depends on its exact nature. For example, fixing _Vulnerable and Outdated Components_ is process-driven, requiring discipline in managing versions and retiring older ones. Some, however, are technical and only require proper configuration in the reverse proxy or API Gateway, _e.g._, _Server Side Request Forgery_. +A WAF addresses only part of the threat model. The [API gateway security guide](/learning-center/api-gateway-security/) places request filtering alongside authentication, authorization, rate limiting, mTLS, and service-level controls. + ## Nobody cares about security Security is a touchy subject because hardening security doesn't bring any value to the business. Career-driven managers won't care about security as they won't be able to showcase they increased the company's profit by X% on their next yearly evaluation. Unless the board considers security seriously, chances are nobody will care. For this reason, most organizations implement checkbox-based security, aka plausible deniability. If you're interested in implementing security properly, I've w [...] diff --git a/blog/en/blog/2025/02/21/why-reinvent-api-gateways.md b/blog/en/blog/2025/02/21/why-reinvent-api-gateways.md index 93f837827c7..ca827a90fc1 100644 --- a/blog/en/blog/2025/02/21/why-reinvent-api-gateways.md +++ b/blog/en/blog/2025/02/21/why-reinvent-api-gateways.md @@ -110,3 +110,5 @@ Our mission with APISIX was never just about building a product—it was about r With a thriving global community, rapid innovation, and enterprise adoption, Apache APISIX is set to become the de facto API gateway for modern applications. Whether you're a startup, enterprise, or open-source enthusiast, if you're looking for a high-performance, cloud-native API gateway, we invite you to explore APISIX. + +For a criteria-based evaluation of Apache APISIX, Kong, Envoy, and Traefik, see the [open-source API gateway comparison](/learning-center/open-source-api-gateway-comparison/).